
The average cost for organizations in the United States reached a staggering $11.5 million per data breach incident in 2026. For a local business, a single regulatory slip-up or security gap isn’t just a technical glitch; it’s an existential threat to everything you’ve built. We understand that keeping up with shifting standards feels like a full-time job you didn’t apply for. That’s why professional IT compliance services Houston business owners trust are no longer a luxury. They’re a foundational requirement for staying operational and avoiding the massive inflation-adjusted fines now being handed out by the OCR.
You likely feel the pressure of the February 2026 HIPAA update or the confusion surrounding the July suspension of CMMC Phase 2 requirements. It’s frustrating to manage complex documentation when you’d rather focus on your growth. This guide provides a practical roadmap to help you secure a clean audit report and potentially exempt your business from high cyber insurance premiums. We’ll walk through the current 2026 regulatory landscape, from PCI DSS 4.0 enforcement to the Texas Data Privacy and Security Act, ensuring your data remains locked down and your peace of mind stays intact.
Key Takeaways
- Learn why professional IT compliance services Houston are now a core requirement for obtaining affordable cyber insurance and maintaining operational stability in 2026.
- Identify the critical 2026 deadlines for HIPAA and CMMC 2.0 that specifically impact healthcare providers and Department of Defense contractors in the local region.
- Master a 5-step assessment process to uncover vulnerabilities in your network infrastructure before they lead to regulatory fines or system downtime.
- Discover how aligning with regulatory frameworks strengthens your business continuity plan, protecting your reputation while lowering emergency technical expenses.
- Understand how a structured 90-day IT needs assessment provides a clear, documented path to regulatory success without disrupting your daily operations.
What are IT Compliance Services and Why Do Houston Firms Need Them?
Providing professional IT compliance services Houston businesses rely on starts with a clear definition. Compliance is the active process of aligning your technology systems with specific legal, industry, and state regulations. While it sounds like a technical hurdle, it’s actually a framework for operational stability. In 2026, the landscape has shifted significantly. We’ve seen that cyber insurance providers now act as the primary enforcers of these standards. If your firm doesn’t meet their rigorous checklists, you’re either denied coverage or hit with premiums that can cripple a small business. For firms in the Greater Houston area, non-compliance leads to more than just fines; it leads to catastrophic downtime that erodes customer trust and halts revenue.
The Distinction Between Security and Compliance
It’s a common mistake to assume that if your network is secure, you’re also compliant. Think of security as the heavy lock on your office door. Compliance, however, is the detailed logbook that records exactly who entered, when they arrived, and what they touched. A simple firewall isn’t enough to pass a cybersecurity assessment Houston firms face today. You need Regulatory compliance documentation to prove those tools are working as intended and that your business follows established protocols. We use network monitoring to provide the real-time data and system health dashboards required for these audits. This ensures you aren’t just safe; you’re audit-ready.
Key Drivers for Compliance in 2026
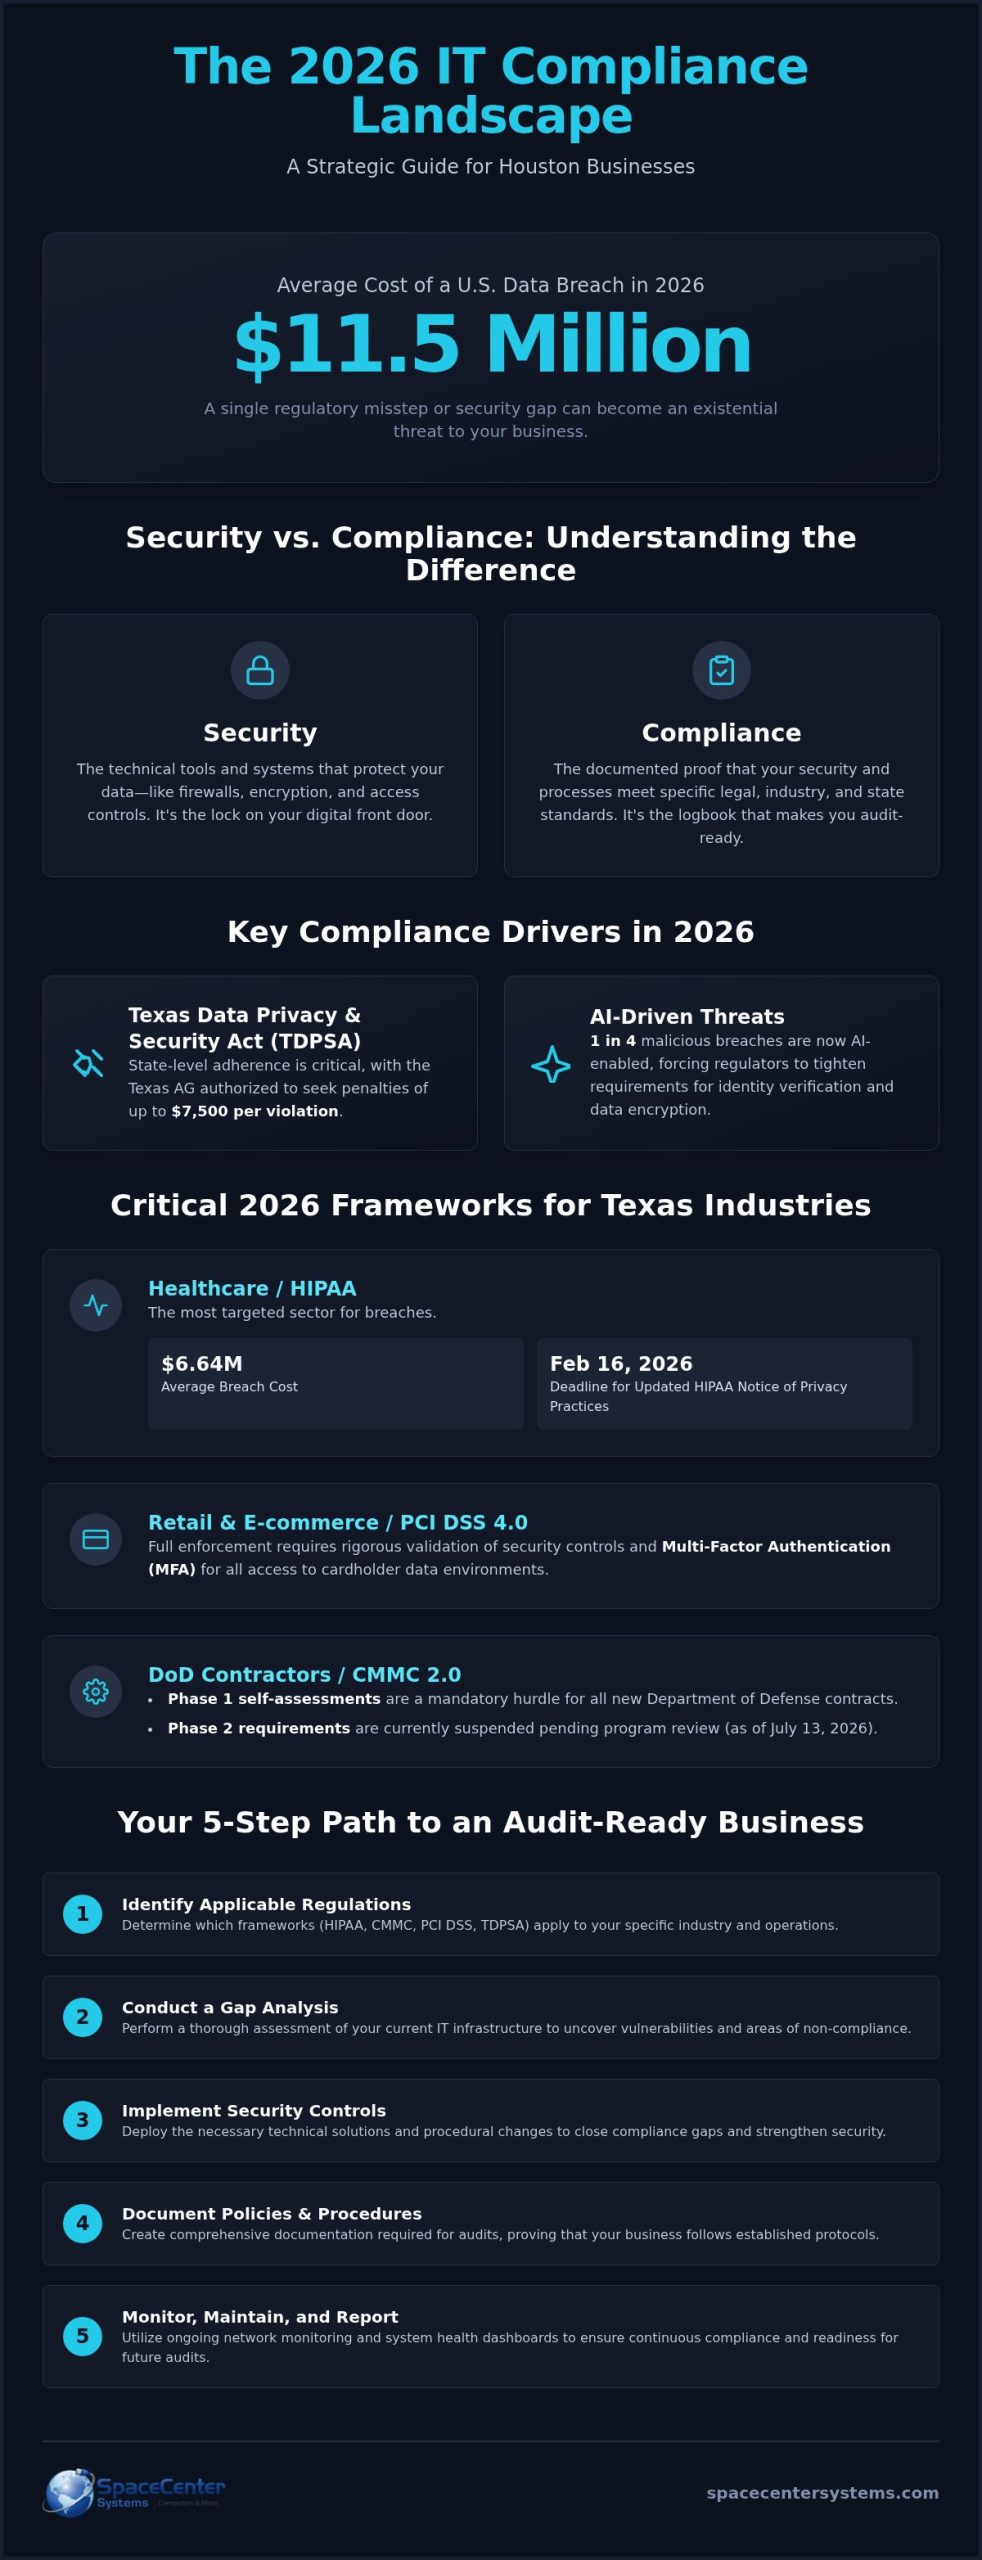
The Texas Data Privacy and Security Act (TDPSA) is now a major factor for local businesses. The Texas Attorney General has the authority to seek civil penalties of up to $7,500 per violation, making state-level adherence just as critical as federal mandates. AI-driven threats are also forcing regulators to tighten their requirements. One in four malicious breaches in 2026 are now AI-enabled, leading to stricter rules regarding identity verification and data encryption. The “set it and forget it” mentality is your biggest risk. Compliance isn’t a one-time project. It’s an ongoing commitment to stability that requires specialized IT compliance services Houston providers offer to navigate these shifting 2026 standards. By maintaining a clean compliance record, you protect your business from the $11.5 million average cost of a U.S. data breach and ensure your operations remain resilient against modern threats.
Critical Compliance Frameworks for Texas Industries
Houston’s economic landscape is diverse, stretching from the high-tech Energy Corridor to the specialized medical hubs in Pearland and Sugar Land. Each sector faces a unique set of regulatory hurdles that demand precision. For retail and e-commerce firms, the full enforcement of PCI DSS 4.0 as of March 31, 2025, remains a top priority. This standard requires rigorous validation of security controls and multi-factor authentication for all access into the cardholder data environment. Utilizing expert IT compliance services Houston providers offer helps local businesses manage these requirements without disrupting daily sales operations.
Healthcare IT and HIPAA in Houston
Healthcare continues to be the most targeted sector for data breaches, with the average cost of an incident reaching $6.64 million in 2026. Medical clinics, dental practices, and senior living facilities must stay ahead of federal deadlines, such as the February 16, 2026, requirement to update HIPAA Notice of Privacy Practices. Implementing IT support for healthcare offices is essential for maintaining patient trust. Beyond basic encryption, your facility needs robust backup solutions to ensure that life-critical medical records are always accessible, even during a system failure or local disaster.
CMMC and NIST for Houston Manufacturing
The Department of Defense supply chain in Houston is currently adjusting to the phased implementation of CMMC 2.0. While Phase 2 requirements were suspended on July 13, 2026, pending a program review, Phase 1 self-assessments remain a mandatory hurdle for new contracts. Many local contractors align their operations with the NIST Cybersecurity Framework to establish a baseline of reliability. Our manufacturing IT support bridges the gap between vulnerable shop floor equipment and secure office networks. By documenting network integrity and access controls now, your firm stays audit-ready for when full implementation resumes. If you are unsure where your current infrastructure stands, you can schedule a consultation to review your specific industry requirements.
Adhering to these frameworks isn’t just about avoiding the OCR’s four-tier penalty structure, where willful neglect can lead to annual caps of over $2.1 million. It’s about building a resilient business that can withstand the AI-driven phishing and deepfake threats that have become common in 2026. Whether you are managing patient records or government blueprints, a structured approach to compliance ensures your technology supports your growth instead of creating a liability.
The 5-Step Process for an IT Compliance Assessment
Achieving regulatory success isn’t a matter of luck; it requires a repeatable, documented methodology. Navigating these requirements requires the structured IT compliance services Houston businesses use to maintain their reputations and avoid costly penalties. We follow a clear, five-step path to move your organization from vulnerability to verified compliance.
- Step 1: Inventory and Asset Discovery – We begin by mapping every device on your networking infrastructure. You cannot protect or audit hardware that hasn’t been identified.
- Step 2: Gap Analysis – We compare your current technical environment against specific mandates, such as the HIPAA Security Rule. This identifies exactly where your systems fall short of legal requirements.
- Step 3: Technical Remediation – Our team implements the necessary fixes. This includes hardening firewalls, enabling encryption, and optimizing server management to close the gaps found in step two.
- Step 4: Policy Documentation – We help you create the “paper trail” auditors demand. Technical security is only half the battle; you must have written procedures that prove your adherence to the law.
- Step 5: Continuous Monitoring – Compliance is not a one-time event. Transitioning to managed IT services provides the 24/7 oversight needed to remain compliant as standards evolve in 2026.
Bridging the Gap: From Audit to Action
Assessment data is only valuable if it leads to meaningful change. We turn raw audit data into a prioritized project list that addresses your most critical risks first. This includes tackling the human element through security awareness training. Given that phishing remains a top threat, robust business email security is essential for protecting your staff from AI-driven social engineering attacks that bypass traditional filters.
Physical Security Compliance
Many local firms overlook the fact that physical access is a core compliance requirement. An unsecured server room is a direct violation of most major frameworks. We integrate access control and surveillance to provide a complete audit trail of who physically interacts with your hardware. Even your structured cabling Houston installations must meet specific safety and security codes to ensure long-term stability and pass a rigorous physical IT audit. This comprehensive approach ensures your IT compliance services Houston strategy covers every possible entry point for a data breach.
Turning Compliance into Business Continuity and Resilience
Many Houston business owners view audits as a painful necessity. However, the most successful firms use these requirements as a blueprint for disaster recovery planning. When you align with a framework, you aren’t just checking a box; you’re building a fortress around your operations. Professional IT compliance services Houston providers help you shift from a reactive “break-fix” model to a proactive, stable environment. This transition offers a distinct competitive advantage. Large corporate clients and government entities prioritize partners who can prove their data is secure. By leading with your compliance status, you turn a technical requirement into a powerful marketing tool for winning high-value contracts.
Financial stability is another direct benefit of a compliance-first mindset. In 2026, cyber insurance carriers demand advanced endpoint protection and documented incident response plans as prerequisites for coverage. Meeting these standards often leads to lower premiums and fewer emergency IT bills. Instead of paying for expensive “firefighting” after a breach, you invest in a steady pulse of maintenance that keeps your network healthy and your budget predictable. This pragmatism appeals to logical decision-makers who want to protect their bottom line.
Risk Prevention and Disaster Recovery
Compliance audits do more than find security holes. They reveal critical weaknesses in your business continuity strategy. For instance, an audit might show that your on-site backups are vulnerable to the same local disasters that threaten your main office. By integrating cloud infrastructure management, we ensure your data is resilient and accessible from anywhere. Our neighborly approach focuses on keeping local businesses running through hurricanes, power outages, or cyberattacks. We treat your stability as our own success, ensuring your team stays productive while your competitors are still trying to recover.
Budgeting for Compliance in 2026
Planning for compliance costs shouldn’t feel like an emergency expense. We help you spread remediation costs over a 12-month period to keep your cash flow predictable. Consider the ROI; preventing a single $50,000 regulatory fine or avoiding a breach that costs $11.5 million on average is a massive win for your bottom line. Local IT consulting provides a level of precision that national, one-size-fits-all providers simply can’t match. We understand the specific economic pressures of the Houston market. This proximity allows us to design IT compliance services Houston firms can actually afford while meeting every 2026 regulatory standard.
Strengthen your business resilience today
Partner with SpaceCenter Systems: Houston’s Local Compliance Authority
SpaceCenter Systems has been a pillar of the regional economy since 1995. With over 25 years of local experience, we’ve grown alongside the businesses we protect. We don’t believe in the distant, impersonal support offered by national helpdesks. Instead, we provide the specialized IT compliance services Houston firms require to thrive in an increasingly regulated market. Our team understands that compliance isn’t just about software; it’s about the physical and technical integrity of your entire operation.
To get started, we offer a unique 90-day IT needs assessment program. This structured approach allows us to deep-dive into your current environment without causing operational friction. We identify every gap, from outdated encryption to messy server rooms, and provide a clear roadmap for the IT compliance services Houston businesses need to reach “Mission Critical” reliability. Our primary service areas include Houston, Pearland, Sugar Land, and League City.
Why Proximity Matters for Compliance
Compliance often requires a physical presence that national firms can’t provide. We perform on-site audits to inspect your server rooms and ensure your cables meet safety and security codes. This hands-on approach is vital for firms in Pasadena and Friendswood who need more than just a remote login. You get direct access to local technicians who understand the Texas business climate and the specific risks our region faces. When an auditor asks for proof of physical access control, we’re there to help you document it.
The SpaceCenter Commitment
Our commitment is to provide practical, real-world technology solutions that make sense for your bottom line. We avoid abstract jargon in favor of clear, active-voice declarations of value. You’ll see this in our system health dashboards and our transparent reporting. We position ourselves as your local partner, invested in your success as much as our own. Our work is polished, professional, and designed to give you peace of mind that your data is secure and your business is audit-ready.
Don’t let shifting 2026 standards leave your business vulnerable to fines or downtime. Experience a more personalized level of support from a seasoned local authority. Schedule your 2026 Compliance Consultation today and secure your roadmap to regulatory success.
Secure Your Competitive Advantage in 2026
Compliance is no longer just a technical hurdle. It’s a foundational part of your business continuity and a powerful tool for winning larger contracts. By following a structured roadmap, you move from the fear of regulatory fines to the confidence of a clean audit report. Professional IT compliance services Houston business owners trust provide more than just documentation; they offer a stable environment where your data remains secure and your operations stay resilient against 2026 threats.
SpaceCenter Systems has been a pillar of the local community since 1995. We bring over 25 years of local expertise to every project, specializing in the specific demands of HIPAA and CMMC compliance. Our unique 90-day IT needs assessment provides a clear, practical path to regulatory success without disrupting your daily work. You deserve the peace of mind that comes from knowing your technology is handled by a seasoned local authority who understands the Texas business climate.
Secure Your Houston Business: Schedule Your IT Compliance Assessment Today
We’re ready to help you turn these complex requirements into a long-term advantage for your firm. Let’s build a more secure and stable future for your business together.
Frequently Asked Questions
What is the average cost of IT compliance services for a Houston small business?
Compliance costs depend on the size of your network and the specific regulatory framework you need to satisfy. Instead of a flat rate, we look at the number of endpoints, the volume of sensitive data, and current security gaps. Starting with a 90-day IT needs assessment allows you to understand your specific requirements before committing to a full remediation plan. This approach ensures your budget is spent on practical, real-world technology solutions that address your actual risks.
How long does a full HIPAA or CMMC compliance audit typically take?
A comprehensive compliance audit typically spans four to twelve weeks, depending on the complexity of your infrastructure. For a local healthcare practice, the process involves reviewing data access logs and physical security; while a defense contractor preparing for CMMC 2.0 may require several months of preparation. We use a structured methodology to ensure no detail is missed. This timeline allows for thorough discovery, gap analysis, and the creation of the mandatory documentation auditors require for a clean report.
Can my current IT company perform a valid compliance assessment?
While your current provider understands your daily operations, a specialized firm provides the objective oversight necessary for a valid audit. Many general IT companies lack the deep expertise required for frameworks like HIPAA or CMMC. Partnering with a dedicated provider of IT compliance services Houston firms have trusted since 1995 ensures you get an unbiased view of your vulnerabilities. We focus on identifying risks that internal teams or general providers might overlook during routine maintenance.
Is IT compliance required for businesses that do not handle medical or credit card data?
Yes, because state laws like the Texas Data Privacy and Security Act (TDPSA) now apply to almost any business collecting personal data from residents. Even if you don’t handle medical records, your cyber insurance carrier likely requires adherence to a recognized framework to maintain coverage. Compliance is now a standard part of business continuity. It protects you from the rising costs of data breaches, which reached an average of $11.5 million per U.S. incident in 2026.
What happens if our Houston business fails a compliance audit?
Failing an audit can lead to massive financial penalties, ranging from inflation-adjusted OCR fines to civil penalties of $7,500 per violation under Texas law. Beyond the immediate fines, your business faces the risk of losing its cyber insurance or being barred from government contracts. We focus on preventing these outcomes by identifying gaps early. Correcting these issues before an official audit protects your reputation and prevents the devastating cost of downtime associated with legal or regulatory intervention.
How often should we conduct an IT compliance review in 2026?
You should conduct a formal IT compliance review at least once a year, though 2026 standards favor continuous monitoring. Major shifts in technology, such as the February 2026 HIPAA update, require immediate adjustments to your policies. If you move offices or roll out new software, an interim assessment is necessary to ensure your security posture remains intact. Regular reviews keep your documentation current and ensure your network monitoring tools are accurately tracking every device on your infrastructure.
Does managed IT support include ongoing compliance monitoring?
Professional managed IT support typically includes the continuous monitoring required to prove ongoing compliance. We use system health dashboards and network monitoring to track data access and security events in real time. This proactive oversight is a core part of the IT compliance services Houston organizations use to stay audit-ready. Instead of a one-time “check-the-box” activity, managed services provide the permanent paper trail and technical safeguards needed to satisfy modern insurance and legal requirements.
Will a compliance audit disrupt my daily business operations?
A well-planned compliance audit will not disrupt your daily business operations. Most of the technical discovery and network mapping happens in the background using non-invasive monitoring tools. We coordinate with your team for brief interviews or physical inspections of server rooms and structured cabling at times that suit your schedule. Our goal is to provide a polished, professional experience that delivers a clear roadmap to success without hindering the productivity of your staff or the care of your patients.